第14章サイバー資源の品質とサイバーコンピューティングのガバナンス
CONCEPTS IN PRACTICE概念を実践する
Think like a Hackerハッカーのように考える
To implement effective cybersecurity policies and procedures, cybersecurity experts need to understand hackers, including how they think and how they are likely to target an organization. What does it mean to think like a hacker?
英語のヒント
効果的なサイバーセキュリティーの方針と手順を実施するには、専門家はハッカーを理解する必要がある。どのように考え、組織をどのように狙いそうかという点も含む。ハッカーのように考えるとは、どういうことだろうか。
Skilled hackers tend to be inquisitive, with an in-depth understanding of technology and its capabilities. They stay abreast of technological advances, including cybersecurity measures. They tend to be creative thinkers with excellent analytical skills, which makes them capable of finding innovative ways to circumvent cybersecurity features and hack into a system. They also tend to understand human nature, including our weaknesses and vulnerabilities.
英語のヒント
熟練したハッカーは好奇心が強く、技術とその能力を深く理解している傾向がある。サイバーセキュリティー対策を含め、技術の進歩に遅れず付いていく。創造的に考え、優れた分析力を持つことが多いため、安全機能を回避してシステムへ侵入する革新的な方法を見つけられる。また、弱さや弱点を含め、人間の性質を理解していることも多い。
To think like a hacker, you must develop these skills and learn to use them with a hacker mindset, constantly reviewing your system and recognizing how it can be hacked. This includes prioritizing security and remaining aware that hackers constantly look for weaknesses that enable them to exploit a system. As part of this, learn about ethical hacking, which includes penetration testing, and use ethical hacking practices to ensure your system is up-to-date and ready to withstand cyberattacks.
英語のヒント
ハッカーのように考えるには、こうした技能を伸ばし、ハッカーの視点で使うことを学ばなければならない。常に自分のシステムを見直し、どう侵入されうるかを認識する。セキュリティーを優先し、ハッカーが悪用できる弱点を絶えず探していると自覚し続けることも含まれる。その一環として、侵入テストを含む倫理的ハッキングを学び、その慣行を使って、自分のシステムが最新で、サイバー攻撃に耐えられるようにしよう。
Domains of Cybersecurity and Associated Cryptography Techniquesサイバーセキュリティーの領域と関連する暗号技術
Cybersecurity includes various domains that comprise overall cybersecurity. Common cybersecurity domains include the following:
サイバーセキュリティーには、全体を構成するさまざまな領域がある。一般的な領域は次のとおりである。
• Protection of computer systems and networks that ensure security at a national scale, economic health, and public safety, called infrastructure security. The National Institute of Standards and Technology (NIST) cybersecurity framework is meant to help organizations in this area. Additional guidance is provided by the U.S. Department of Homeland Security (DHS).
• 国家規模の安全、経済の健全さ、公共の安全を確保するコンピューターシステムとネットワークの保護を、インフラストラクチャーセキュリティーという。米国国立標準技術研究所(NIST)のサイバーセキュリティーフレームワークは、この領域で組織を助けるためのものである。米国国土安全保障省(DHS)も、追加の指針を提供する。
• Protection of wired and wireless (Wi-Fi) computer networks from intrusions, called network security. The designs for operating systems, virtual machines, and monitors must include protections against unauthorized use.
• 有線・無線(Wi-Fi)のコンピューターネットワークを侵入から守ることを、ネットワークセキュリティーという。OS、仮想マシン、モニターの設計には、無許可の利用への防御を含めなければならない。
• Protection of applications on premise and in the cloud, with security integrated during the design phase for data handling and user authentication, called application security. The process of authentication confirms the identity and authorization of people and devices that use a system. Many resources support these efforts, including books and online materials on security engineering, “robust” programming, and secure programming for specific operating systems.
英語のヒント
• オンプレミスとクラウド上のアプリケーションを保護し、設計段階でデータ処理と利用者認証のセキュリティーを組み込むことを、アプリケーションセキュリティーという。認証の過程は、システムを使う人や装置の身元と権限を確認する。セキュリティー工学、「堅牢な」プログラミング、特定のOS向けの安全なプログラミングに関する書籍やオンライン教材など、多くの資源がこの取り組みを支える。
12 IBM. 2023. “Cost of a Data Breach Report 2023. https://www.ibm.com/reports/data-breach. 13 Morgan, Steve. 2024. “Top 10 Cybersecurity Predictions and Statistics for 2024.” Cybercrime Magazine. https://cybersecurityventures.com/top-5-cybersecurity-facts-figures-predictions-and-statistics-for-2021-to-2025/
12 IBM、2023年。「Cost of a Data Breach Report 2023」。https://www.ibm.com/reports/data-breach13 Steve Morgan、2024年。「Top 10 Cybersecurity Predictions and Statistics for 2024」。Cybercrime Magazine。https://cybersecurityventures.com/top-5-cybersecurity-facts-figures-predictions-and-statistics-for-2021-to-2025/
• Protection of the data, digital files, and other information a system maintains, called information security. For example, database systems must protect against SQL injection by ensuring that queries issued to the database do not somehow contain malignant code that could compromise the security of the database and its infrastructure. Information security requires data protection measures, such as the General Data Protection Regulation (GDPR), that secure sensitive data from unauthorized access, exposure, or theft.
英語のヒント
• システムが保持するデータ、デジタルファイルなどの情報の保護を、情報セキュリティーという。例えばデータベースシステムは、データベースへの問い合わせに、そのデータベースと基盤の安全を損なう悪意あるコードが紛れ込まないようにし、SQLインジェクションを防がなければならない。情報セキュリティーには、一般データ保護規則(GDPR)のように、機密データを無許可のアクセス、露出、盗難から守る、データ保護策が必要である。
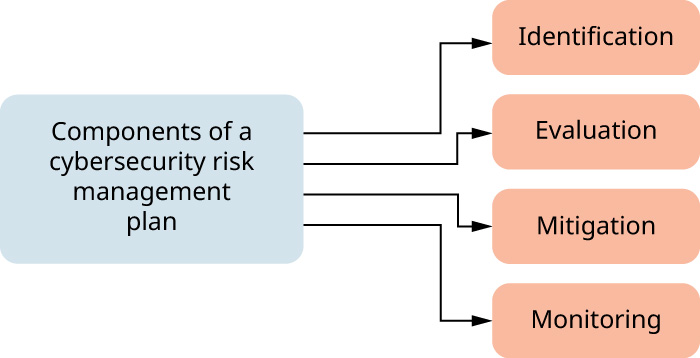
These domains function cooperatively to create a cybersecurity risk management plan (Figure 14.7).
これらの領域は協力して働き、サイバーセキュリティーのリスク管理計画を形作る(図14.7)。
attribution: Copyright Rice University, OpenStax, under CC BY 4.0 license · CC BY 4.0 · Source出典
Figure 14.7 Cybersecurity should be based on a comprehensive risk management plan that identifies and evaluates cybersecurity risks, designs and implements practices to mitigate those risks, and monitors the system and identifies areas that need to be updated. (attribution: Copyright Rice University, OpenStax, under CC BY 4.0 license)
図14.7 サイバーセキュリティーは、包括的なリスク管理計画に基づくべきである。その計画では、危険を特定・評価し、緩和のための慣行を設計・実施し、システムを監視して、更新の必要な領域を特定する。(帰属表示:著作権 Rice University、OpenStax、CC BY 4.0)
An important pillar of cybersecurity assurance is nonrepudiation, which provides proof of data’s origin, authenticity, and integrity. Nonrepudiation is achieved through cryptography using, for example, digital signatures, which are used in online transactions to ensure that a party cannot later deny placing an order or denying its signature’s authenticity. In addition to digital signatures, nonrepudiation is also used in digital contracts and emails. Email nonrepudiation involves methods such as email tracking to assure senders that messages are delivered and also provides recipients with proof of the sender’s identity. This ensures neither party can deny that a message was sent, received, and processed.
英語のヒント
サイバーセキュリティー保証の重要な柱の一つは、否認防止である。データの出所、真正性、完全性の証拠を提供する。デジタル署名などの暗号技術によって実現する。オンライン取引で署名を使うと、当事者が後で注文を否認したり、署名が本物であることを否定したりできないようにする。否認防止は、デジタル署名に加え、電子契約や電子メールにも使われる。メールの追跡などにより、メッセージが届けられたことを送信者に保証し、受信者には送信者の身元の証拠を提供する。そのため、どちらの当事者も、送信、受信、処理が行われたことを否認できなくなる。
Beyond basic securing of information systems, cybersecurity requires creating and governance of processes that protect organizations and individuals against costly breaches. End-user education is a critical part of this process. Organizations must promote security awareness to enhance endpoint security. For example, training users to delete suspicious email attachments and avoid using unknown USB devices can help.
英語のヒント
情報システムを基本的に保護するだけでなく、サイバーセキュリティーには、高くつく侵害から組織と個人を守るプロセスの作成と統制が必要となる。エンドユーザー教育は、その重要な一部である。端末の安全を高めるため、組織はセキュリティー意識を促進しなければならない。例えば、怪しいメール添付を削除し、知らないUSB装置を使わないように教えることが役立つ。
Disaster recovery and business continuity planning are also essential to minimize disruption to key operations. This requires tools and procedures to respond to cybersecurity incidents, natural disasters, and power outages. Data storage is another critical area. Protection measures that promote data resilience with safeguards include encryption and immutable and isolated data copies that can quickly be restored to recover data and minimize the impact of a cyberattack.
英語のヒント
主要な業務への混乱を最小限にするには、災害復旧と事業継続の計画も欠かせない。サイバーセキュリティー事故、自然災害、停電へ対応するツールと手順が必要になる。データ保存も重要な領域である。保護策によってデータの回復力を高める方法には、暗号化と、変更不能で隔離されたデータのコピーがある。素早く復元してデータを取り戻し、サイバー攻撃の影響を最小限にできるようにする。
Evolvability is an important cyber quality, but the evolution of platforms on which information systems may be deployed creates a need for new security measures. For example, mobile solutions security requires specific protection measures to protect applications, containers, and mobile mail. Furthermore, when using the cloud, organizations must ensure confidential computing by encrypting data at rest (i.e., while data are stored in the cloud), during transfer, and during processing. This ensures that processes meet business requirements and regulatory compliance standards and supports customer privacy.
英語のヒント
進化可能性は重要なサイバー品質特性だが、情報システムを配置できるプラットフォームが進化すると、新しい安全対策が必要になる。例えば、モバイルソリューションでは、アプリケーション、コンテナー、モバイルメールを守る特定の対策が必要である。さらにクラウドを使う組織は、保存中、すなわちクラウド内で保管されている間、転送中、処理中のデータを暗号化し、機密性を保った計算を確保しなければならない。これによって、プロセスが業務要件と規制準拠の標準を満たし、顧客のプライバシーを支える。