第6章インフラストラクチャーの抽象化層:オペレーティングシステム
6.6 Reliability and Security6.6 信頼性とセキュリティー
Learning Objectives学習目標
By the end of this section, you will be able to:
この節を終えると、次のことができるようになる。
• Explain how OSs protect computer systems
• OSがコンピューターシステムを保護する仕組みを説明する。
• Discuss key security-related functions of the OS
• OSのセキュリティーに関する主要な機能を論じる。
• Explain how the OS helps the computer system recover from failures
• コンピューターシステムが障害から回復するのを、OSがどのように助けるかを説明する。
• Discuss how advances in technology affect the longevity of an OS
• 技術の進歩がOSの寿命に及ぼす影響を論じる。
Remember that we consider an OS to be reliable if it delivers service without errors or interruptions. In addition to reliability, an OS should provide a high level of protection, security, and stability. Here, we learn about OS protection, security, recovery, and longevity.
英語のヒント
誤りや中断なしにサービスを提供するOSを、信頼できるとみなすことを思い出そう。OSには信頼性に加え、高い保護水準、セキュリティー、安定性も必要である。ここでは、OSの保護、セキュリティー、回復、寿命について学ぶ。
Protection保護
The general mechanism that is used throughout the OS for all resources that need to be protected, such as memory, processes, files, devices, CPU time, and network bandwidth is called protection. The objectives of the protection mechanism are to allow sharing (which in this context means using the hardware to do more than one thing at a time), help detect and contain accidental or unintentional errors, and prevent intentional/ malicious abuses. The main challenge when it comes to protection is that intentional abuse is much more difficult to eliminate than accidents.
英語のヒント
メモリ、プロセス、ファイル、デバイス、CPU時間、ネットワーク帯域幅など、保護が必要なすべてのリソースに対し、OS全体で使う一般的な仕組みを、保護という。保護の仕組みの目的は、共有を認め、偶発的・非意図的な誤りの検出と封じ込めを助け、意図的・悪意ある不正利用を防ぐことである。ここでの共有とは、ハードウェアで一度に複数のことを行うという意味だ。保護の主な課題は、意図的な不正利用をなくすことが、事故をなくすよりもはるかに難しいことである。
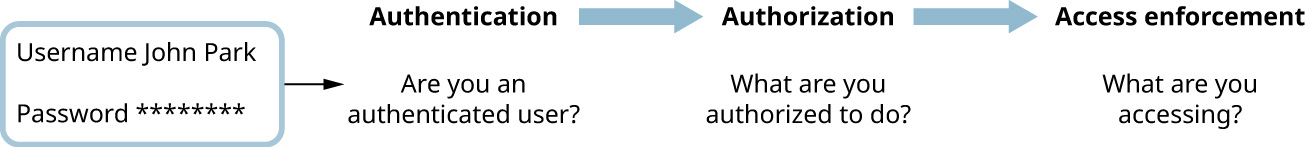
There are three aspects to a protection mechanism: authentication, authorization, and access enforcement. Authentication identifies a responsible party or principal behind each action, authorization determines which principals are allowed to perform which actions, and access enforcement controls access using authentication and authorization information. A tiny flaw in any of these areas can compromise the entire protection mechanism. It is extremely difficult to make all these protection mechanism techniques operate in such a way that there are no loopholes that can be exploited by adversaries. Figure 6.36 illustrates the relationship between authentication, authorization, and access enforcement.
英語のヒント
保護の仕組みには、認証、認可、アクセス制御の強制という三つの側面がある。認証は、各動作の背後にある責任を持つ当事者、つまり主体を識別する。認可は、どの主体にどの動作を認めるかを決める。アクセス制御の強制は、認証と認可の情報を使ってアクセスを制御する。これらのどの領域でも、ごく小さな欠陥によって、保護の仕組み全体が損なわれる可能性がある。攻撃者が悪用できる抜け穴をなくす形で、保護を構成するすべての技術を動作させることは、極めて難しい。図6.36は、認証、認可、アクセス制御の強制の関係を示す。
attribution: Copyright Rice University, OpenStax, under CC BY 4.0 license · CC BY 4.0 · Source出典
Figure 6.36 The first step of the protection mechanism is authentication, which checks the username and password; then comes authorization, which checks the privileges; and, finally, there is access enforcement, which controls access. (attribution: Copyright Rice University, OpenStax, under CC BY 4.0 license)
図6.36 保護の最初の段階は認証で、ユーザー名とパスワードを確認する。次は認可で、特権を確認する。最後に、アクセスを制御するアクセス制御の強制がある。(出典:著作権 Rice University、OpenStax。CC BY 4.0ライセンス)
Securityセキュリティー
The process of checking to see if a user’s credentials match the credentials in a database of authorized users or in a data authentication server is called authentication. The traditional means of authentication involves the user providing a password, which is a secret piece of information that is used to establish the identity of a user and should be relatively long and hard to guess. Most systems store the passwords in a password database. A password database must be protected because it is vulnerable most of the time. For example, both organizations and users should avoid storing passwords in a directly readable form.
英語のヒント
利用者の認証情報が、認められた利用者のデータベースや、データ認証サーバーの認証情報と一致するかを調べる処理を、認証という。従来の認証方法では、利用者がパスワードを提示する。パスワードは、利用者の身元を確かめるための秘密の情報であり、比較的長く、推測しにくいものにする必要がある。大半のシステムは、パスワードをパスワードデータベースに保存する。パスワードデータベースは脆弱な状態にあることが多いため、保護しなければならない。たとえば、組織も利用者も、パスワードをそのまま読める形で保存することを避けるべきである。
An alternate form of authentication involves using a badge or key. The badge is a logical access system. The badge does not have to be kept secret. It can be counterfeit, but if it is, the owner will know. The badge must be cheap to make but hard to duplicate.
英語のヒント
別の認証方法では、バッジや鍵を使う。バッジは、論理的なアクセスシステムである。バッジ自体を秘密にしておく必要はない。偽造される可能性はあるが、偽造されれば所有者には分かる。バッジは、安く作れ、しかも複製が難しいものでなければならない。
Another form of authentication is two-factor authentication, which involves two factors: the system calls or texts a user’s phone for the traditional password during login, employing the cell phone as a key. For example, a site sends a text message to a user’s phone with a one-time passcode. The user must read the passcode from the phone and type it into the login page.
英語のヒント
認証の別の方法が、二つの要素を使う二要素認証である。ログイン時に、従来のパスワードのため、システムが利用者の電話へ電話やテキストメッセージを送り、携帯電話を鍵として使う。たとえば、サイトがワンタイムパスコードを、テキストメッセージで利用者の電話へ送る。利用者は、そのパスコードを電話で読み、ログインページへ入力しなければならない。
In two-factor authentication, an attacker must have both your password and cell phone to hijack your account. This approach is particularly effective for authenticating to websites, as the requiring of both the password and the physical cell phone is a sufficient deterrent. To enhance efficiency, the two-factor authentication process can be optimized for websites. Once the authentication is completed, a cookie is loaded into your browser. This cookie then transforms your browser into a type of key, granting you the ability to log in with the password as long as the cookie persists.
英語のヒント
二要素認証では、攻撃者がアカウントを乗っ取るには、パスワードと携帯電話の両方が必要になる。パスワードと物理的な携帯電話の両方を要求することが十分な抑止となるため、この方法は、ウェブサイトでの認証に特に有効である。効率を高めるため、二要素認証の手順をウェブサイト向けに最適化できる。認証が完了すると、ブラウザーにCookieを読み込む。このCookieはブラウザーを一種の鍵へ変え、Cookieが残っている限り、パスワードでログインできるようにする。
Whenever a user needs to log in from a different browser or different machine, two-factor authentication is used again. After logging in, the user id is associated with every process executed under that login because the user id is stored in the process control block and children inherit the user id from their parents. Once authentication is complete, the next step of protection is authorization.
英語のヒント
別のブラウザーや別のマシンからログインする必要があるたびに、再び二要素認証を使う。ログイン後は、そのログインのもとで実行するすべてのプロセスに、ユーザーIDを結び付ける。ユーザーIDがプロセス制御ブロックに保存され、子は親からユーザーIDを引き継ぐからである。認証が終わると、次の保護の段階は認可となる。
The process of determining the relationship between principals, operations, and objects by defining the kind of principals that are allowed to carry out a specific activity with a defined set of objects is called authorization. These principals are represented using a matrix that includes an entry for each principal and a column for each object as a representation of authorization information on given operations. For example, defining who has the authorization to read/view, edit, or delete the file. Each entry in the access matrix describes the capability of each principal over each one of the objects. When the matrix includes all of the principals and all of the assigned objects, it can become complex and hard to manage. The ideal way to solve this problem is to use a guideline such as an access control list. An access control list (ACL) is a set of guidelines that outline the authority of each user (i.e., which user is permitted access to given resources). An ACL controls the access and privileges using a matrix design.
英語のヒント
定められた対象の集合に対し、特定の動作を実行してよい主体の種類を定め、主体、操作、対象の関係を決める処理を、認可という。主体は、各主体の項目と各対象の列を持つ行列によって表され、所定の操作に対する認可情報を示す。たとえば、誰にファイルの読み取り・閲覧、編集、削除の権限があるかを定める。アクセス行列の各項目は、各主体が各対象に対して何をできるかを表す。すべての主体と、割り当てられたすべての対象を行列へ含めると、複雑になり、管理が難しくなることがある。この問題の理想的な解決法は、アクセス制御リストのような指針を使うことである。アクセス制御リスト(ACL)は、各利用者の権限、つまり、どの利用者が所定のリソースへアクセスできるかを定める指針の集合である。ACLは、行列の設計を使って、アクセスと特権を制御する。
The ACL from Oracle features the assignment of users to roles such as basic users, advanced users, customer administrator, among others. A role is configured to confer privileges on objects rather than attaching privileges to individual users, as this would be much more difficult to set up and maintain. The most general form of setting privileges is creating a list of user and privilege pairs, which is called a capability list. A capability list is a list of objects and operations for each user that defines the user rights and capabilities. Typically, capabilities also act as names for objects, which means the list cannot even name objects not referred to in your capability list. For simplicity, users can be organized into groups with a single ACL entry for an entire group, and each group can be made to share the same privileges. While in Windows OS, ACLs are very general, they are relatively simple in UNIX/Linux. For example, in UNIX/Linux, access can be read, write, and execute, and it can be granted to the file owner, the file owner’s group, or “the world” of all users. In many cases, the user root has full privilege for all of the operations and has access to all of the permissions. For example, the user root can view, edit, and delete a file. ACLs are straightforward and can be utilized by any file systems in Windows. The utilization involves sharing a namespace at a high level of visibility by making it public, while defining another namespace as private—akin to the encapsulation of objects in object-oriented programming.
英語のヒント
OracleのACLには、基本ユーザー、上級ユーザー、顧客管理者などの役割へ利用者を割り当てる機能がある。個々の利用者へ特権を付ける方法は、設定と維持がずっと難しいため、役割を通して対象への特権を与えるように構成する。特権を設定する最も一般的な形は、利用者と特権の組の一覧を作ることであり、これをケイパビリティリストという。これは、利用者ごとの対象と操作の一覧で、利用者の権利と権限を定める。通常、ケイパビリティは対象の名前としても働くため、自分のケイパビリティリストに記されていない対象は、名前で指定することすらできない。単純にするため、利用者をグループにまとめ、グループ全体で一つのACL項目を使い、各グループで同じ特権を共有させることができる。Windows OSのACLは非常に汎用的であるのに対し、UNIX/Linuxでは比較的単純である。たとえばUNIX/Linuxのアクセスには、読み取り、書き込み、実行があり、ファイルの所有者、所有者のグループ、または全利用者という「世界」に認めることができる。多くの場合、rootユーザーは、すべての操作について完全な特権を持ち、すべての許可にアクセスできる。たとえばrootは、ファイルの閲覧、編集、削除ができる。ACLは分かりやすく、Windowsのどのファイルシステムでも使える。その利用では、一つの名前空間を公開して広く見える状態で共有し、別の名前空間を非公開と定める。これは、オブジェクト指向プログラミングにおけるオブジェクトのカプセル化に似ている。
One component of an OS must be in charge of enforcing access rules and safeguarding authentication and authorization to provide a high level of security. The system’s access enforcement mechanism has complete authority; therefore, it must be simple in programming and small in size. The security kernel is a substitute approach that is composed of hardware and software and serves as the OS’s inner protection layer. Generally, any kind of management such as memory and interrupt management are provided by a security kernel.
英語のヒント
高いセキュリティーを提供するには、OSの一つの構成要素が、アクセス規則の強制と、認証・認可の保護を担当しなければならない。システムのアクセス制御を強制する仕組みは、完全な権限を持つ。そのため、プログラムが単純で、規模も小さくなければならない。セキュリティーカーネルは、ハードウェアとソフトウェアから構成され、OS内部の保護層として働く、別の方法である。一般に、メモリ管理や割り込み管理など、あらゆる種類の管理が、セキュリティーカーネルによって提供される。